


The best Nightfall alternatives for 2026: 1. Enigma Vault NoPII, 2. Microsoft Purview DLP, 3. Netskope One DLP, 4. Cyberhaven, 5. Forcepoint DLP, 6. Proofpoint Enterprise DLP, 7. Mimecast Incydr, 8. Zscaler DLP, 9. DTEX, 10. Cisco Cloudlock.
Nightfall is an AI-native data loss prevention platform for SaaS apps, endpoints, browsers and email, with AI agent and MCP controls on top and Developer APIs for scanning data from your own code. Nightfall itself publishes head-to-head pages against all nine competitors below (source), and Gartner Peer Insights lists five of them as Nightfall alternatives (source).
If what you need to protect is the customer data your own application sends to an LLM, the best alternative is Enigma Vault NoPII, which publishes every plan and starts free. If you need company-wide DLP for employees and SaaS apps, these are the strongest options:
- Microsoft Purview DLP: Best for organizations standardized on Microsoft 365 (G2 rating 4.6 from 23 reviews)
- Netskope One DLP: Best for teams that want DLP inside a SASE platform (G2 rating 4.4 from 98 reviews, platform-wide)
- Cyberhaven: Best for tracing data lineage across endpoints and AI tools (G2 rating 4.5 from 19 reviews)
- Forcepoint DLP: Best for regulated teams that need deep policy templates (G2 rating 4.3 from 45 reviews)
Every rating in this guide links to the product’s G2 or Capterra page, and every review quote links to the review itself.
Top 10 Alternatives to Nightfall at a Glance
| Provider | Best for | How it protects data | Deployment | Starting price | G2 rating | Our score (/5) |
|---|---|---|---|---|---|---|
| Enigma Vault NoPII | Keeping PII Out of Your Own LLM API Calls | Tokenizes PII in LLM API traffic, restores it | Hosted proxy; self-hosted on Enterprise | Free, then $49/mo | 5.0/5 (1) | 3.8 |
| Microsoft Purview DLP | Organizations Standardized on Microsoft 365 | Policy DLP across Microsoft 365 and devices | Microsoft 365 and endpoints | Microsoft licensing | 4.6/5 (23) | 3.6 |
| Netskope One DLP | Teams That Want DLP Inside a SASE Platform | Inline DLP in a SASE platform | Netskope cloud and endpoint | Contact sales | 4.4/5 (98) | 3.4 |
| Cyberhaven | Tracing Data Lineage Across Endpoints and AI Tools | Lineage-based DLP and insider risk | Endpoint agent | Contact sales | 4.5/5 (19) | 3.4 |
| Forcepoint DLP | Regulated Teams That Need Deep Policy Templates | Template-driven multi-channel DLP | Cloud, web, email, endpoint | Request pricing | 4.3/5 (45) | 3.2 |
| Proofpoint Enterprise DLP | Organizations Where Email Is the Main Leak Path | Email-centric DLP with insider risk | Email, cloud, endpoint | Contact sales | 4.3/5 (61) | 3.1 |
| Mimecast Incydr | Insider Risk Detection Across Endpoint, Browser and Email | Behavioral exfiltration detection | Endpoint agent, cloud, email | Contact sales | 4.2/5 (72) | 3.1 |
| Zscaler DLP | Zscaler Customers Extending Inline Protection | Inline DLP with EDM and OCR | Zscaler cloud and endpoint | Contact sales | No reviews yet | 2.9 |
| DTEX | Insider Risk Programs Built on Behavioral Intelligence | Behavioral insider risk scoring | Endpoint telemetry and cloud | Contact sales | No reviews yet | 2.7 |
| Cisco Cloudlock | API-Based CASB and DLP for Cloud Apps | API-based CASB and DLP | Cloud-native, API-based | Cisco sales | No reviews yet | 2.6 |
Protect the prompts your product sends. Enigma Vault NoPII tokenizes PII before it reaches the model provider and restores it in the response. Your first million protected tokens each month are free.
TL;DR
- Enigma Vault NoPII (3.8/5): Replaces Nightfall’s Developer API job for your own LLM calls; free tier, then $49 a month.
- Microsoft Purview DLP (3.6/5): The consolidation choice for Microsoft 365 shops, with Windows and macOS endpoint coverage.
- Netskope One DLP (3.4/5): Inline DLP and GenAI guardrails for teams already routing traffic through Netskope.
- Cyberhaven (3.4/5): Lineage-based DLP that shows where data came from before it left.
- Forcepoint DLP (3.2/5): Template-heavy DLP for regulated teams, at the cost of more tuning.
- Proofpoint Enterprise DLP (3.1/5): Email-first DLP with insider risk, best if you already use Proofpoint.
- Mimecast Incydr (3.1/5): Insider risk and source code exfiltration detection with forensic detail.
- Zscaler DLP (2.9/5): Inline DLP with Exact Data Match and OCR for existing Zscaler customers.
- DTEX (2.7/5): Behavior-first insider risk scoring across users, data and AI activity.
- Cisco Cloudlock (2.6/5): API-based CASB and DLP for cloud apps, closest to Nightfall’s SaaS model.
Why Teams Look for Nightfall Alternatives
Nightfall earns its ratings: A G2 reviewer praises its AI coverage and strong out-of-the-box policies, and it rates 4.6 on G2 from 101 reviews. The reasons buyers still evaluate alternatives are about price visibility, scope and investigation workflow.
- The price comes after a sales call: Nightfall prices its Foundation and Premier editions per user, per year, and the amounts are not on the pricing page. Final pricing depends on user count and data volume (source).
- There is no self-serve trial: Nightfall offers a free 7-day proof of value instead (source), so you cannot test it on your own data without a scoped engagement.
- The platform may be bigger than the job: Foundation covers all supported SaaS apps, an endpoint agent for two devices per user and 150 GB of data-at-rest discovery, and Premier adds hooks for Cursor, Claude Code and VS Code, MCP discovery and an MCP gateway (source). A team that only needs to scrub its own application’s prompts pays for a lot it will not use.
- Reviewers want better triage: A G2 reviewer says reporting and filters need much more improvement for analyzing events, and asks for a better analyst triage experience (source).
If those points match your evaluation, the alternatives below sort by which part of Nightfall they replace.
First, Decide Which Nightfall Job You Are Replacing
Nightfall does two different jobs, and most teams only need to replace one. Picking the wrong category is the most common mistake in this search.
| If the risk is… | You need | Start with |
|---|---|---|
| Employees sharing data in SaaS apps, email or on laptops | Company-wide DLP | Purview, Cisco Cloudlock, Netskope, Forcepoint or Proofpoint |
| Insiders moving files, code or customer data off devices | Endpoint DLP and insider risk | Cyberhaven, Mimecast Incydr or DTEX |
| Traffic you already inspect inline | DLP inside your security service edge | Netskope or Zscaler |
| Your own application sending customer data to an LLM API | An LLM privacy proxy | Enigma Vault NoPII |
Some companies need both: A DLP platform for employees and a proxy for the AI features they build. The two do not overlap, because a proxy only sees traffic your application routes through it.
How We Scored These Nightfall Alternatives
We scored every provider on the same six criteria, weighted for a team replacing some or all of Nightfall. Weights sum to 100%, and the score in the table is the weighted result.
- Pricing transparency and time to start (25%): Whether you can see a price and test on your own data without a sales cycle.
- AI data protection (25%): Coverage of prompts, uploads, model responses, agents and MCP.
- Channel coverage (15%): SaaS apps, endpoints, email and browsers.
- Deployment effort (15%): How much you install and tune before data is protected.
- Detection and remediation (10%): Classification quality, blocking, redaction and investigation depth.
- Review evidence (10%): Rating and number of verified reviews on G2 and Capterra.
Weight channel coverage higher and Netskope, Forcepoint and Purview lead; weight pricing transparency higher and Enigma Vault NoPII stays on top.
The 10 Best Nightfall Competitors and DLP Alternatives
Each entry covers what the product is, which part of Nightfall it replaces, what it costs, where it falls short, and what verified reviewers say.
- Starting price
- Free, then $49 a month
- Free tier or trial
- Lite: 1M protected tokens a month, no card
- Deployment
- Hosted proxy; self-hosted edition on Enterprise
- What it replaces from Nightfall
- The Developer API job: Scanning what your own application sends to model providers, with real values restored in the response
Enigma Vault NoPII is an LLM privacy proxy. Your application points its model client at the NoPII base URL; NoPII swaps names, emails, account numbers and secrets for deterministic tokens before the request reaches OpenAI, Anthropic or another provider, then restores the real values in the response.
For a Nightfall buyer, NoPII replaces one specific part of the platform: The Developer APIs (formerly Firewall for AI) that teams call to scrub prompts (source). It does not replace Nightfall’s SaaS, endpoint or email coverage, and our own NoPII page says so plainly: If the problem is employees pasting data into chatbots across hundreds of SaaS apps, you need endpoint data loss prevention.
Key features
- Base-URL integration: Point your model client at NoPII; no scan calls to add around each request
- Deterministic tokens: The same customer becomes the same token in every turn and document, so the model keeps context
- Round trip: Real values are restored before your user sees the answer
- Agent and RAG coverage: System prompts, tool-call arguments and results, and the embeddings endpoint
- Detection: 11 entity types on by default, 25+ to opt into, and 14 pattern families of credentials and API keys
- Fail-closed: If tokenization fails at any step, the request is blocked and never forwarded
Pricing
| Plan | Price | Protected tokens a month | Beyond the allowance |
|---|---|---|---|
| Lite | $0 | 1M (hard cap) | Upgrade prompt |
| Starter | $49/mo | 50M | $1.00 per million |
| Growth | $249/mo | 500M | $0.80 per million |
| Business | $499/mo | 2B | $0.60 per million |
| Enterprise | Custom | Custom commit | Negotiated or waived; includes the self-hosted edition |
Yearly billing saves on Starter, Growth and Business, and a BAA is available on NoPII Enterprise (pricing page).
Pros
- You can price the whole year before talking to anyone: Every tier is on the pricing page, and the free tier does not expire.
- Answers stay readable, because real values come back in the response instead of placeholders.
- A detection failure blocks the request, so nothing leaks on a best-effort basis.
Cons
- It only sees traffic your application routes through it, so Slack, Google Drive, email and laptops stay out of scope.
- It scans text only; images, audio and files need their text extracted first.
- Names and places are detected in English and Hindi; pattern-based identifiers work in most languages.
What users say
- Reviews: One G2 review so far: NoPII has a single 5/5 review on G2, written by a member of the Enigma Vault marketing team, so we do not quote it. The wider Enigma Vault listing has 6 reviews on G2.
Rated 5.0/5 on G2 from 1 review. No Capterra listing.
Watch for: Count where your Nightfall alerts come from. If most are SaaS or endpoint events, NoPII covers a small part of the problem.
See it on a real message in the NoPII live demo, or read our Enigma Vault NoPII vs Nightfall comparison.
See what reaches your model provider. Send a message with a name, email or SSN in the NoPII live demo and compare what your backend, the model provider and NoPII each receive.
2. Microsoft Purview DLP: Best for Organizations Standardized on Microsoft 365
- Starting price
- Through Microsoft 365 licensing
- Free tier or trial
- Free trial from the Purview page
- Deployment
- Microsoft 365, Windows and macOS devices, file shares
- What it replaces from Nightfall
- SaaS and endpoint DLP where most sensitive data already lives in Exchange, SharePoint, OneDrive and Teams
Microsoft Purview DLP applies data loss prevention policies to Microsoft 365 locations such as Exchange and SharePoint, and to locations you add: On-premises file shares, endpoint devices and non-Microsoft cloud apps. Nightfall publishes its own head-to-head page against it (source), and Gartner lists it among Nightfall’s alternatives (source).
For a Nightfall buyer in a Microsoft shop, the case is consolidation: The policy engine sits inside licenses you may already own, so the question becomes whether it reaches the non-Microsoft apps and AI tools Nightfall covers today.
Key features
- Microsoft 365 coverage: Policies for Exchange, SharePoint, OneDrive and Teams, managed from one Purview portal
- Endpoint DLP: Protects Windows 10, Windows 11 and the three most recent macOS versions
- Extended locations: On-premises file shares and non-Microsoft cloud apps can be added to the same policies
- Sensitive information types: Built-in types for common identifiers, plus custom types you define
- AI coverage: Microsoft says policies span cloud apps, email, devices and AI in one place
Pricing
| Option | Price | Notes |
|---|---|---|
| Purview DLP | Through Microsoft 365 licensing | No standalone DLP price on the product page |
| Trial | Free trial | Offered on the Purview product page |
| Enterprise agreement | Contact Sales | For volume licensing |
Pros
- If you already pay for the right Microsoft 365 tier, the incremental cost can be low compared with a separate per-user DLP contract.
- Reviewers like how easy it is to create custom sensitive information types.
- One portal covers email, files and Windows and macOS devices.
Cons
- Reviewers say a production rollout needs proper planning, and rules cannot be bulk-edited through PowerShell.
- Activity exports cap at 10,000 items at a time, per one reviewer, which slows investigations at scale.
- Licensing is harder to compare line by line with Nightfall’s per-user quote.
What users say
- Likes: Flexible detection: A reviewer finds it easy to create custom sensitive information types (source), and another says it detects many types of private data across locations (source).
- Dislikes: Rollout effort and limits: Reviewers report it is tough to take into production without planning (source), that rules cannot be bulk-updated through PowerShell (source), and that activity export caps at 10,000 items (source).
Rated 4.6/5 on G2 from 23 reviews. Capterra lists Microsoft Purview Data Loss Prevention with no reviews.
Watch for: List the non-Microsoft SaaS apps and AI tools Nightfall monitors today, and confirm each one is reachable from Purview before you retire Nightfall.
3. Netskope One DLP: Best for Teams That Want DLP Inside a SASE Platform
- Starting price
- Contact sales
- Free tier or trial
- Demo
- Deployment
- Netskope One cloud platform, inline and endpoint
- What it replaces from Nightfall
- Inline DLP for web, SaaS, endpoints and GenAI, enforced in the same platform as web and cloud access
Netskope One DLP is the data loss prevention service inside Netskope’s security platform. It classifies PII, card numbers, financial data and intellectual property automatically and applies guardrails across cloud, web, endpoint and AI environments. Nightfall compares itself against it directly (source), and Gartner lists it among Nightfall’s alternatives (source).
For a Nightfall buyer, Netskope is the architectural opposite: Enforcement happens inline as traffic passes through the platform, rather than through API connections to each SaaS app.
Key features
- Automated discovery: Finds PII, payment card numbers, financial information and intellectual property on-premises and in the cloud
- GenAI guardrails: Stops employees pasting sensitive code or data into AI models while still letting them use the tools
- Behavior analytics: AI-driven UEBA tightens enforcement when a user’s actions look risky, such as bulk downloads before leaving
- DSPM and DLP together: Posture management and DLP in a single architecture
- Platform coverage: Cloud, endpoint and AI environments from the Netskope One platform
Pricing
| Option | Price | Notes |
|---|---|---|
| Netskope One DLP | Quote | Sold as part of the Netskope One platform |
Pros
- If you already route traffic through Netskope, DLP becomes a policy decision rather than a new deployment.
- Behavior-aware enforcement adds context that content scanning alone misses.
- Reviewers value having CASB, secure web gateway and DLP in one place.
Cons
- Reviewers describe the initial setup and policy configuration as complex, which is a big change from an API-first tool.
- G2 does not rate Netskope One DLP on its own; the 98 reviews cover the whole platform.
- No published pricing.
What users say
- Likes: One platform for many controls: A reviewer values bringing CASB, secure web gateway and other controls together (source), and another points to its deep inline visibility (source).
- Dislikes: Complex setup: Reviewers call setup and policy configuration complex (source), and one wants simpler troubleshooting and more customizable reports (source).
G2 rates the Netskope One Platform 4.4/5 from 98 reviews; there is no separate DLP listing. Capterra rates the Netskope One Platform 4.0 from 656 reviews.
Watch for: If you only need DLP, a full security service edge rollout is a much larger change than swapping one API-based tool for another.
- Starting price
- Contact sales
- Free tier or trial
- Demo
- Deployment
- Endpoint coverage on Windows, Mac, Linux and VDI
- What it replaces from Nightfall
- Endpoint exfiltration prevention and insider risk, with the history of where each piece of data came from
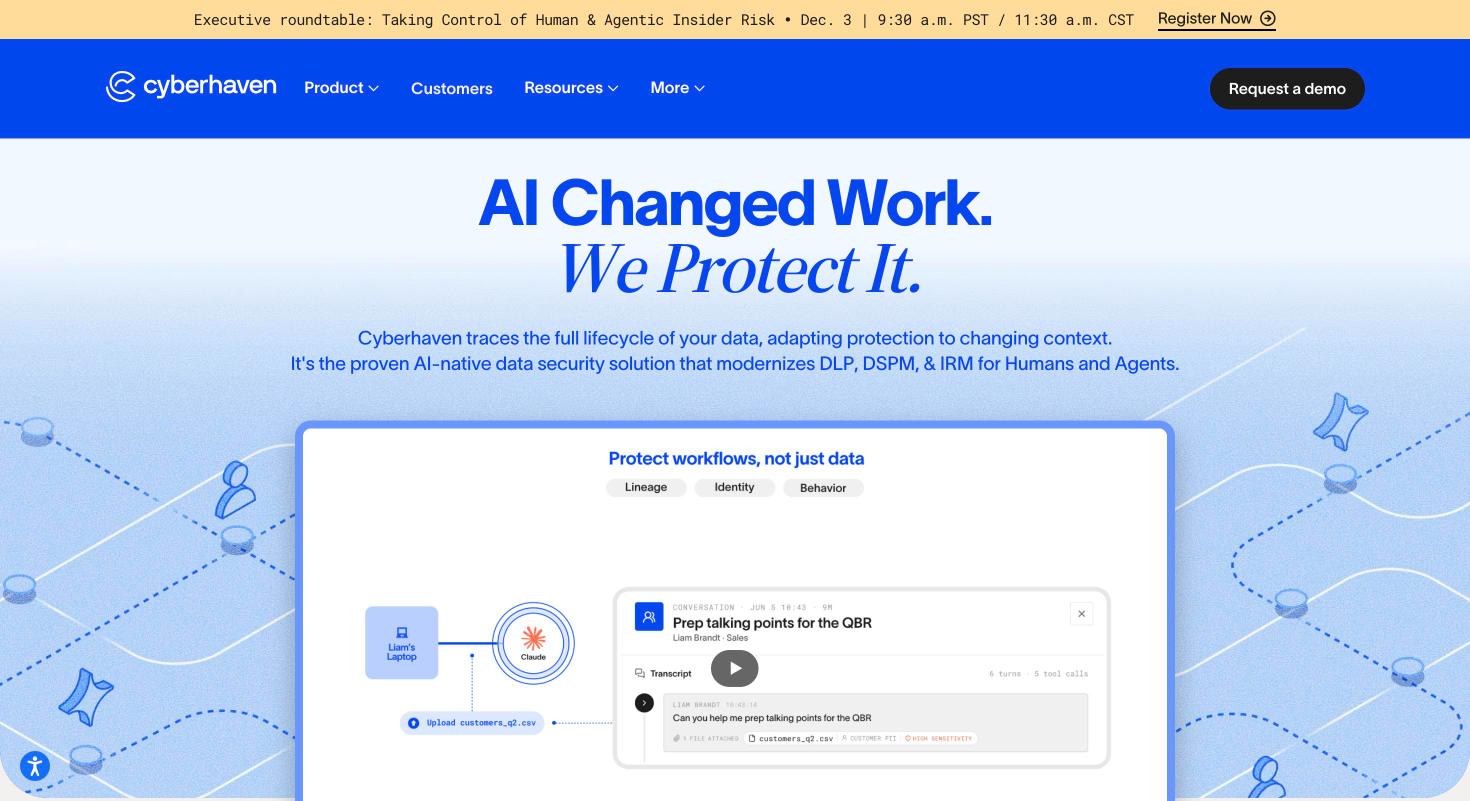
Cyberhaven describes itself as an AI-native data security platform that modernizes DLP, DSPM and insider risk management for people and agents. Its core idea is data lineage: It traces content from its origin through every paste, copy and rewrite, so protection follows the data rather than the file. Nightfall publishes a head-to-head page against it (source).
For a Nightfall buyer, Cyberhaven makes sense when the worry is data leaving through laptops, USB drives and AI tools, and you want to see how it got there before deciding whether it was a leak.
Key features
- Data lineage: Traces content from its origin through every paste, copy and rewrite by people and agents
- Shadow AI control: Finds unsanctioned AI tools, stops sensitive data reaching prompts, uploads and agents, and reports on AI usage
- Coding agent governance: Controls agents such as Claude Code and Cursor
- Exfiltration blocking: USB, printer, email, personal cloud and uploads to unsanctioned web, SaaS and AI apps
- Endpoint coverage: Windows, Mac, Linux and VDI
- Insider risk and DSPM: Discovers and classifies exposed data across cloud, endpoint and workflows
Pricing
| Option | Price | Notes |
|---|---|---|
| Cyberhaven platform | Quote | Demo request on the website |
Pros
- Lineage tells an analyst whether a file started as customer data, which content-only scanning cannot.
- Covers Windows, Mac, Linux and VDI from one agent family.
- A reviewer notes that user-based risk scoring is included without an extra subscription.
Cons
- One reviewer finds Linux coverage behind Windows and Mac, with some policies not applying.
- Another says setup takes time to integrate fully, so plan for a longer rollout than Nightfall’s.
- No published pricing.
What users say
- Likes: Real-time tracking and clear policies: A reviewer singles out real-time data tracking and mapping (source), and another likes seeing every policy laid out graphically (source).
- Dislikes: Linux parity and setup time: One reviewer finds Linux coverage behind Windows and Mac (source), and another says setup could be simpler (source).
Rated 4.5/5 on G2 from 19 reviews. No Capterra listing.
Watch for: It is an endpoint-led platform, so map your device fleet and operating systems before the trial.
5. Forcepoint DLP: Best for Regulated Teams That Need Deep Policy Templates
- Starting price
- Request pricing
- Free tier or trial
- Demo
- Deployment
- Cloud, web, email and endpoint channels
- What it replaces from Nightfall
- Policy-driven DLP across email, web, cloud and endpoints, with templates for industry and regional rules
Forcepoint DLP unifies data security for AI, cloud, web, email and endpoint with real-time enforcement and pre-defined compliance templates. Nightfall compares itself against it directly (source), and Gartner lists it among Nightfall’s alternatives (source).
For a Nightfall buyer, Forcepoint trades setup speed for depth: More policy detail and channel coverage, with more tuning work up front.
Key features
- Multi-channel enforcement: One policy set for AI, cloud, web, email and endpoint
- Compliance templates: Pre-defined templates for industry and regional rules such as GDPR and CCPA
- ARIA assistant: An AI assistant that surfaces insights, recommends protection and deploys policies from a chat interface
- AI Mesh classification: Discovers and classifies structured and unstructured data across data stores
- Risk-adaptive policies: Adjusts enforcement automatically as a user’s behavior changes
- Cloud DLP: Extends protection for Google Workspace and Microsoft 365
Pricing
| Option | Price | Notes |
|---|---|---|
| Forcepoint DLP | Request Pricing | Start Today route on the product page |
Pros
- Pre-built templates shorten the work of mapping policies to specific regulations.
- Reviewers praise centralized visibility across endpoints, email, web and cloud.
- Rated 4.5 on Capterra from 17 reviews, alongside 4.3 on G2.
Cons
- Reviewers consistently describe initial setup and policy configuration as complex.
- Some alerts need extra tuning before they are useful, according to a reviewer.
- No published pricing.
What users say
- Likes: Centralized visibility: Reviewers value centralized visibility across endpoints, email, web and cloud (source) and strong control across channels (source).
- Dislikes: Complex setup and tuning: Reviewers report complex initial setup and policy configuration (source) and alerts that need extra tuning (source).
Rated 4.3/5 on G2 from 45 reviews and 4.5/5 on Capterra from 17 reviews.
Watch for: Budget analyst time for policy tuning in the first months; every reviewer we read mentions it.
6. Proofpoint Enterprise DLP: Best for Organizations Where Email Is the Main Leak Path
- Starting price
- Contact sales
- Free tier or trial
- Demo
- Deployment
- Email, cloud, endpoint and web channels
- What it replaces from Nightfall
- DLP and insider risk analysis, built around email and extended to cloud, endpoint and GenAI
Proofpoint Enterprise DLP positions itself as data loss prevention for people, data and AI. It applies one set of policies and classifiers across channels and pairs DLP with insider risk analysis. Nightfall publishes a head-to-head page against it (source), and Gartner lists it first among Nightfall’s alternatives (source).
For a Nightfall buyer that already uses Proofpoint for email security, this is the consolidation option.
Key features
- GenAI controls: Detects and controls sensitive data in prompts and uploads, including unsanctioned AI tools
- Unified policies: Applies the same policies and data classifiers across channels from one platform
- Insider risk analysis: Analyzes activity and data flows to identify exfiltration and insider risk
- Threat intelligence: Uses AI and threat intel to assess data risk
- Email DLP: Built on Proofpoint’s email security, alongside cloud and endpoint
Pricing
| Option | Price | Notes |
|---|---|---|
| Enterprise DLP | Quote | Demo request and How to Buy |
Pros
- One vendor for email security and DLP removes an integration.
- Reviewers say it prevents incidents well once policies are crafted correctly.
- Alerts show who did what, which reviewers find helpful for triage.
Cons
- A reviewer reports many false positives on the PCI rule, including matches in file metadata.
- Another says the API documentation needs a lot of work, which matters if developers will call it.
- No published pricing.
What users say
- Likes: Effective once tuned: A reviewer says it prevents DLP incidents well once policies are crafted correctly (source), and another likes how alerts show who and what each one is about (source).
- Dislikes: False positives and API docs: One reviewer gets many false positives around the PCI rule (source), and another says the API documentation needs a lot of work (source).
Rated 4.3/5 on G2 from 61 reviews. Capterra lists it with no reviews.
Watch for: Run your own PCI sample through it during the trial; that is where reviewers report the most noise.
7. Mimecast Incydr: Best for Insider Risk Detection Across Endpoint, Browser and Email
- Starting price
- Contact sales
- Free tier or trial
- Demo
- Deployment
- Lightweight endpoint agent for Mac, Windows and Linux, plus cloud and email
- What it replaces from Nightfall
- Exfiltration detection and investigation across endpoint, browser, cloud sync, email and AI tools
Mimecast Incydr began as Code42 Incydr; code42.com now redirects to Mimecast’s data protection page. It uses behavioral, context-driven detection to catch exfiltration across endpoints, cloud, email and AI tools, and records each file movement with who moved it and where it went. Nightfall compares itself against it under the Code42 name (source).
For a Nightfall buyer, Incydr suits a security team that cares most about departing employees and source code leaving, and wants forensic detail for each event.
Key features
- Endpoint agent: A lightweight agent for Mac, Windows and Linux
- Exfiltration detection: USB, browser, cloud sync, AirDrop, Git and GenAI destinations
- Source code protection: Records the file, repository, destination and user when code goes to personal or untrusted destinations
- Watchlists: Monitors departing and high-risk users, with dashboards and alerting
- Investigation: Forensic search, case management and Instructor coaching for users
- Integrations: 350+ integrations, plus API and MCP connections
Pricing
| Package | Price | What it includes |
|---|---|---|
| Data Protection for email | Quote | Outbound email inspection, admin hold, forensic search and an Investigation Agent with 50 AI credits a month; requires Mimecast Apex Email and Collaboration Security |
| Package with endpoint | Quote | Adds exfiltration detection on every endpoint |
Pros
- Reviewers say it gives useful visibility quickly, with a lot of context in one interface.
- The lightweight agent covers Windows, Mac and Linux.
- Source code and Git destinations are first-class detection channels.
Cons
- A reviewer says it is stronger on detection than prevention.
- Another notes preventative controls block by destination or application, with content-aware blocking less granular.
- No published pricing.
What users say
- Likes: Fast, useful visibility: A reviewer likes how quickly it provides genuinely useful visibility (source), and another values how much information it brings together without cluttering the interface (source).
- Dislikes: Detection over prevention: One reviewer finds it stronger on detection than prevention (source), and another wants more granular content-aware blocking (source).
Rated 4.2/5 on G2 from 72 reviews. No Capterra listing.
Watch for: If blocking in the moment matters more than investigation, test its preventative controls on your top exfiltration paths.
- Starting price
- Contact sales
- Free tier or trial
- Demo
- Deployment
- Zscaler cloud inline, with a lightweight endpoint agent
- What it replaces from Nightfall
- DLP inspection for web, email and endpoints inside the Zscaler zero trust platform
Zscaler DLP delivers DLP inspection across web and email traffic and extends it to endpoints with a lightweight agent. Its classification includes Exact Data Match, Indexed Document Matching and OCR for images. Nightfall publishes a head-to-head page against it (source), and Gartner lists Zscaler among Nightfall’s alternatives (source).
It makes most sense for a Nightfall buyer whose traffic already flows through Zscaler, where DLP is an extension of an existing platform.
Key features
- Unified DLP: One policy across web, endpoint and email
- Exact Data Match: Fingerprints specific records, such as customer data, to cut false positives
- Indexed Document Matching and OCR: Classifies documents and text inside images, including images embedded in Word files
- Endpoint DLP: A lightweight agent with process-level context
- GenAI protection: Supports safe GenAI workflows, per Zscaler’s data protection page
Pricing
| Option | Price | Notes |
|---|---|---|
| Zscaler DLP | Quote | Request a demo or contact sales |
Pros
- Exact Data Match lets you fingerprint your own customer records instead of relying on patterns alone.
- OCR covers sensitive data inside images and embedded screenshots.
- No new traffic path if you already run Zscaler.
Cons
- Zscaler DLP has no G2 reviews yet, so there is little independent feedback.
- Outside an existing Zscaler deployment, it is a platform purchase rather than a point tool.
- No published pricing.
What users say
- Reviews: No reviews yet: Zscaler DLP has no G2 reviews yet, so ask for reference customers.
No G2 reviews yet for Zscaler DLP. Capterra lists Zscaler Internet Access but not Zscaler DLP.
Watch for: Confirm how data at rest inside SaaS apps is covered, since inline inspection sees traffic in transit.
9. DTEX: Best for Insider Risk Programs Built on Behavioral Intelligence
- Starting price
- Contact sales
- Free tier or trial
- Demo
- Deployment
- Endpoint telemetry with a cloud platform
- What it replaces from Nightfall
- Insider risk detection that scores behavior across users, data and AI activity, rather than scanning content alone
DTEX describes itself as a risk-adaptive security platform that unifies human, data and AI risk through behavioral intelligence. It collects more than 500 metadata elements and correlates activity across devices into one risk score. Nightfall publishes a head-to-head page against it (source).
For a Nightfall buyer, DTEX is the choice when the main question is intent: Whether a user is malicious, careless or compromised, before any file leaves.
Key features
- Behavioral risk scoring: Correlates more than 500 metadata elements across devices into one risk score
- Behavioral domains: More than 12 human-driven domains, tuned by AI modeling to reduce noise
- Baselines: Profiles behavior by role, department and geography, and separates human from AI activity
- AI Risk Management: Tracks risk created by AI usage and agentic workflows
- AI analysts: A multi-agent triage system and a Deep Researcher hunting agent
- Services: Insider Investigations and Intelligence (i3) from DTEX’s own team
Pricing
| Option | Price | Notes |
|---|---|---|
| DTEX platform | Quote | Request a demo |
| i3 services | Quote | Insider investigations and intelligence |
Pros
- Behavior-first detection tells malicious, careless and compromised activity apart, which content scanning cannot.
- DTEX says it identifies outlier behavior within 10 days of deployment.
- An in-house investigations team is available as a service.
Cons
- It is an insider risk platform first, so in-app SaaS remediation is not its focus the way it is for Nightfall.
- DTEX has no reviews on G2 or Capterra, so there is no independent feedback to weigh.
- No published pricing.
What users say
- Reviews: No reviews yet: DTEX inTERCEPT is listed on G2 and DTEX Systems on Capterra, both with no reviews, so ask for reference customers.
No reviews on G2 or Capterra yet.
Watch for: If your Nightfall use is mostly SaaS remediation, check how DTEX handles data already exposed inside cloud apps.
10. Cisco Cloudlock: Best for API-Based CASB and DLP for Cloud Apps
- Starting price
- Through Cisco sales
- Free tier or trial
- Trials and demos through Cisco
- Deployment
- Cloud-native, API-based
- What it replaces from Nightfall
- API-based DLP and app control for sanctioned cloud apps, the part of Nightfall that scans SaaS data
Cisco Cloudlock is a cloud-native cloud access security broker that uses APIs to manage risk in your cloud app ecosystem. Its DLP continuously monitors cloud environments with out-of-the-box and custom policies. Nightfall publishes a head-to-head page against it (source).
For a Nightfall buyer, Cloudlock is the closest architectural match on SaaS: Both connect to cloud apps through APIs rather than proxying traffic.
Key features
- API-based CASB: Connects to cloud apps through APIs, with no proxy in front of users
- Cloud DLP: Continuously monitors cloud environments with out-of-the-box and custom policies
- User behavior analytics: Flags anomalies, activity outside allowed countries and impossible travel
- Apps Firewall: Discovers apps connected to your cloud accounts, with a crowd-sourced Community Trust Rating
- App control: Ban or allowlist connected apps based on risk
Pricing
| Option | Price | Notes |
|---|---|---|
| Cloudlock | Through Cisco sales | How to Buy and Trials and Demos routes on Cisco’s site |
Pros
- API-based like Nightfall’s SaaS coverage, so no proxy sits in front of users.
- Apps Firewall adds control over third-party apps connected to your cloud accounts.
- A fit for organizations already buying security from Cisco.
Cons
- It covers cloud apps; endpoints and AI tools on devices need other products.
- Cloudlock has no product listing on G2 or Capterra, so independent reviews are hard to find.
- No published pricing.
What users say
- Reviews: No review-site listing: Cisco Cloudlock has no product listing on G2 or Capterra, so ask Cisco for reference customers.
No G2 or Capterra product listing.
Watch for: Check which of your SaaS apps Cloudlock connects to, and plan separate endpoint coverage if Nightfall’s agent is in use today.
Nightfall vs Enigma Vault NoPII
These are different products that overlap on one job: Keeping sensitive data out of the prompts your own application sends to a model. Here is how they line up on that job.
| Nightfall | Also considerEnigma Vault NoPII | |
|---|---|---|
| What it is | DLP platform with Developer APIs for scanning and redaction | LLM privacy proxy for your application’s model calls |
| How you integrate | Call the scan APIs from your code | Point your model client at the NoPII base URL |
| What the model receives | What your code sends after redaction | Deterministic tokens; real values restored in the response |
| Pricing | Per user, per year, through sales | Free for 1M tokens a month, then $49, $249, $499 |
| Trial | Free 7-day proof of value | Free Lite plan that does not expire |
| SaaS, endpoint and email DLP | Yes | No |
| Next step | Live in minutes with a base-URL change. |
Nightfall covers far more surface. NoPII does one job, protecting the LLM traffic your applications generate, with a price you can read before you talk to anyone.
How to Choose a Nightfall Alternative
Where do your alerts come from today? Pull a month of Nightfall events by source. Mostly SaaS points to Purview, Netskope or Forcepoint; mostly endpoint points to Cyberhaven or Incydr; mostly your own AI features points to NoPII.
What does your network already run? If traffic goes through Netskope or Zscaler, adding DLP there is a policy change. If you are Microsoft 365 end to end, Purview is the first comparison your finance team will ask for.
Do you need to block or to investigate? Forcepoint and Netskope lean toward enforcement; Cyberhaven and Incydr lean toward context and forensics.
How much tuning can you staff? Reviewers of almost every enterprise DLP platform here mention policy tuning. If you have one analyst, weigh that more than the feature list.
Best Nightfall Alternative by Scenario
| Scenario | Best pick | Why |
|---|---|---|
| AI features in your own product | Enigma Vault NoPII | Tokenizes PII in prompts, tool calls and embeddings and restores it in responses |
| Microsoft 365 shop | Microsoft Purview DLP | Policies inside Exchange, SharePoint, OneDrive, Teams and Windows and macOS devices |
| Already on a security service edge | Netskope One DLP | Inline DLP in the platform that already carries your traffic |
| Data leaving through laptops and AI tools | Cyberhaven | Lineage across Windows, Mac, Linux and VDI |
| Strict regulatory policies | Forcepoint DLP | Pre-defined templates for industry and regional compliance |
| Email is the main leak path | Proofpoint Enterprise DLP | Email-centric DLP with insider risk |
| Departing employees and source code | Mimecast Incydr | Detection for Git, USB, AirDrop and cloud sync, with forensics |
| Existing Zscaler customer | Zscaler DLP | Exact Data Match and OCR inside the platform you run |
| Insider intent and behavior | DTEX | Behavioral risk scoring that separates malicious, careless and compromised users |
| API-based SaaS coverage on Cisco | Cisco Cloudlock | API-based CASB with DLP and app control |
What Moving Off Nightfall Actually Involves
- Export your detection rules first: Nightfall policies, custom detectors and exclusions do not import into another product. Write them down while you still have access.
- Map each integration: Nightfall connects to SaaS apps through APIs. Inline platforms such as Netskope and Zscaler see traffic differently, so check each app one by one.
- Plan the endpoint swap: Two endpoint agents on the same device can conflict. Agree the order of removal and install with IT.
- Re-baseline your noise: A new classifier produces a new set of false positives. Expect a tuning period before alert volumes settle.
- Move API callers separately: If your developers call Nightfall’s scan APIs, that code path changes independently of the employee DLP rollout.
Try Enigma Vault NoPII on Your Own Traffic
If the part of Nightfall you are replacing is the API that scrubs your application’s prompts, you can prove NoPII on your own traffic before you talk to anyone. The free plan is a permanent tier, not a trial, and moving an existing integration onto it is a base-URL change.
| What the free Lite plan includes | Detail |
|---|---|
| Protected tokens | 1M a month, hard cap, no credit card |
| Model providers | Every supported provider, including OpenAI, Anthropic and Google Gemini |
| Protection | PII detection and tokenization, with values restored in the response |
| Audit | Full audit trail with 7-day log history |
| Limits | 1 workspace, 1 user, 25 custom terms, 60 requests a minute per key, 1-day token retention |
| Upgrade path | Starter at $49 a month for 50M tokens, with no re-integration |
How to run a fair test in a week
- Pick one AI feature: Choose the feature that sends the most customer data to a model today, such as a support assistant or a summarizer.
- Point it at NoPII: Change the model client’s base URL to NoPII in a staging environment. No other code changes are needed.
- Send real-shaped traffic: Replay a sample of production prompts, including tool calls and any embeddings requests.
- Check what left your system: Compare what your backend sent with what the model provider received in the audit trail. Every name, email and account number should arrive as a token.
- Check the answers: Confirm your users still see real values in the responses, and that answers read as well as before.
- Decide with numbers: Use the token count from the trial to price the right plan before anyone signs anything.
When NoPII is not the right fit: If most of your risk is employees sharing data in SaaS apps, email or on laptops, NoPII will not see that traffic, and one of the DLP platforms above is the better choice. Many teams run both: A DLP platform for employees, and NoPII for the AI features they build.
See what reaches your model provider.
Book a demo to map your AI data path, or try the live demo first. If a DLP platform on this list fits you better, we will say so.
More comparisons: Enigma Vault NoPII vs Nightfall AI, Protecto alternatives and Limina alternatives.


